CYBERVOC / Configuration
Infrastructure as code security
Find risky defaults and insecure configuration in the files that define how your application runs.
Run your free scanSupported configuration
Terraform, Kubernetes manifests, Helm charts, Dockerfiles and CloudFormation templates. Checks depend on the supported resource types and configuration available in the repository.
Risks worth catching early
Publicly exposed storage, overly permissive access rules, missing encryption and insecure container settings are examples of detectable misconfigurations.
Scan before deployment
Include infrastructure files in your repository scans. Review the affected configuration and available guidance, then validate changes before deploying.
Configuration is code, too
One workflow for your project.
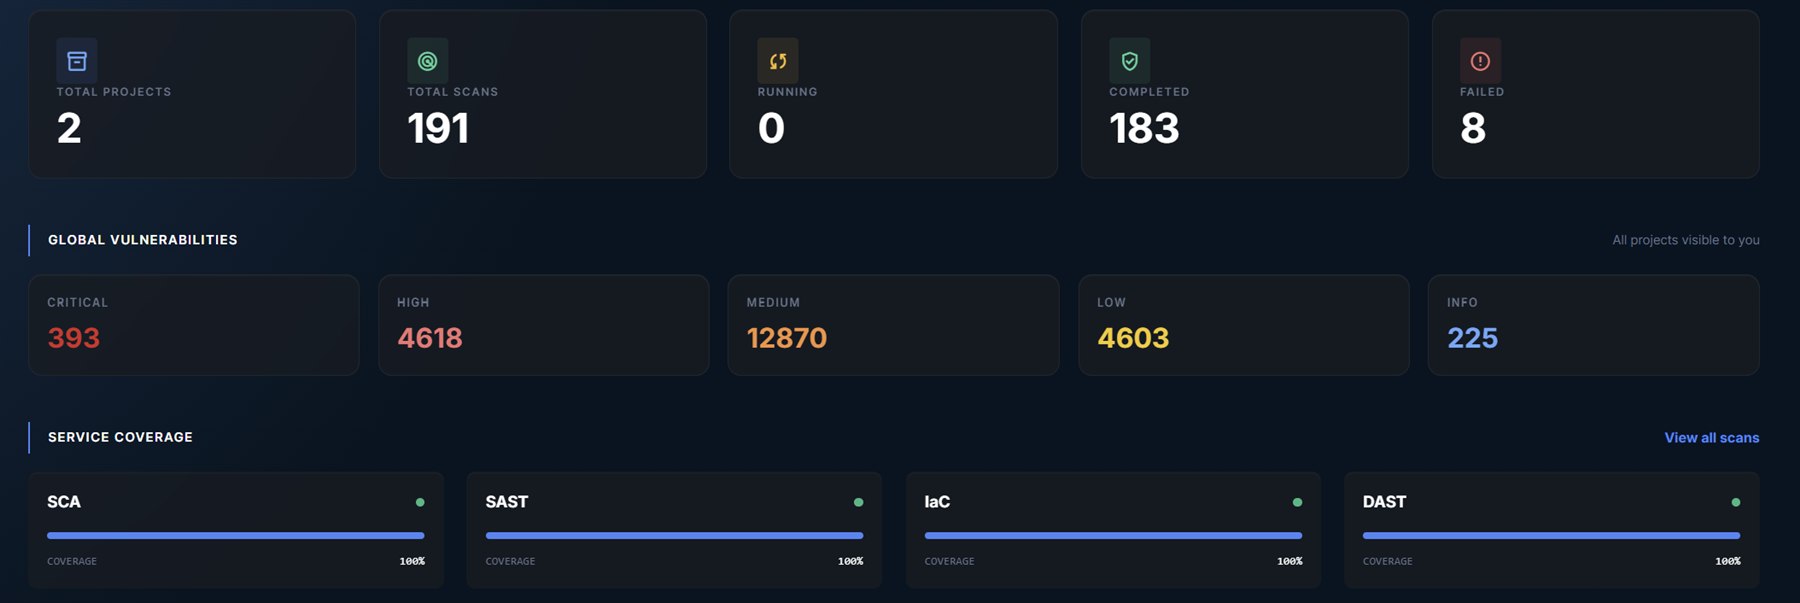
Keep configuration findings alongside source-code and dependency results. Export a PDF to share the details and available remediation guidance.
Read about supported formats →