CYBERVOC / Source code
Static application security testing
Find insecure patterns in the code you write. Investigate findings with their file locations and available remediation guidance.
Run your free scanWhat it looks for
Injection risks, unsafe deserialization, weak cryptography and insecure handling of data, according to the rules available for your language.
Languages
JavaScript, TypeScript, Python, Java, Go, C#, PHP and Ruby. Coverage varies with the language, framework and enabled rules; no static scan guarantees that all vulnerabilities will be found.
Your development workflow
Connect a GitHub or GitLab repository, choose a branch and run a scan. Configure a recurring schedule to check your code as it evolves.
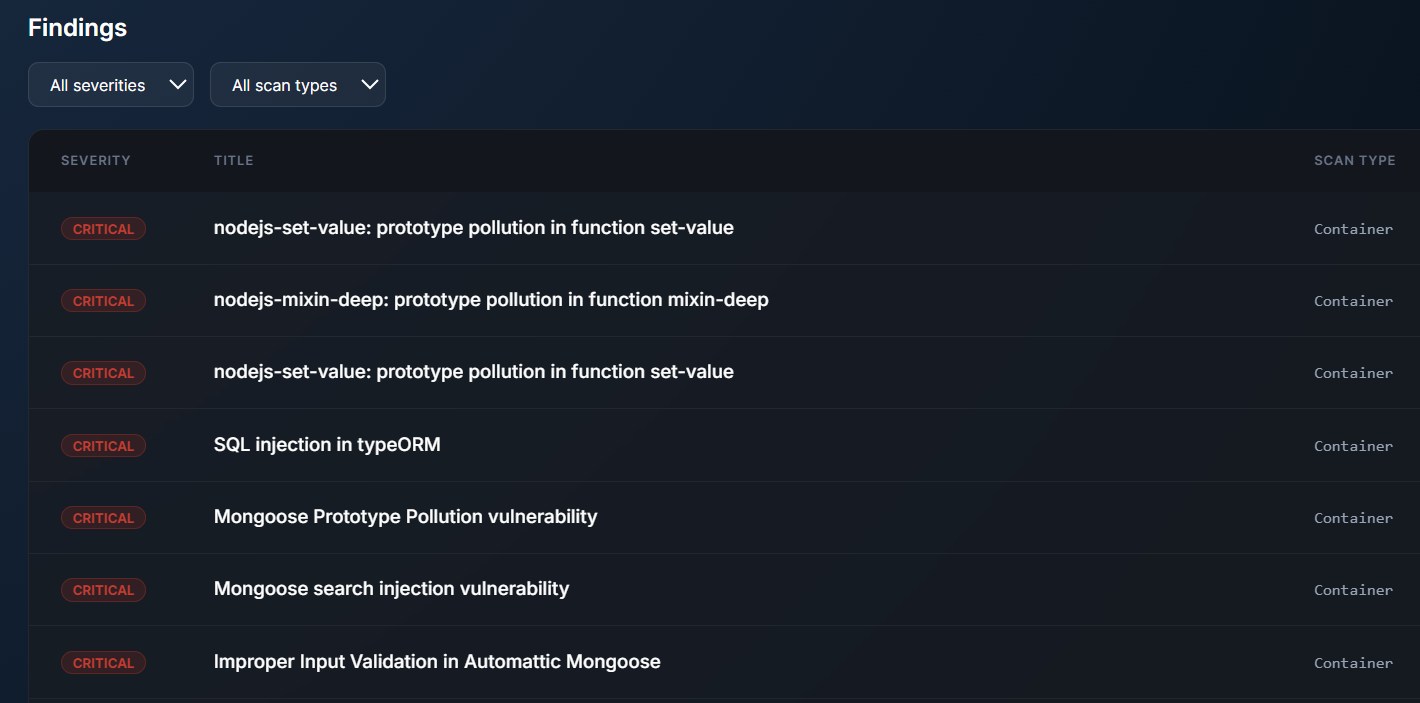
Findings you can work with
Bring the context to your next fix.
Review results in CYBERVOC and export a PDF with vulnerability details and available fix guidance. Share it with your team or an external AI coding agent, then review and test any proposed change.
Read about PDF reports →