CYBERVOC / Dependencies
Software composition analysis
Your application includes more than your own code. Find known vulnerabilities in the packages it depends on.
Run your free scanRecognize vulnerable packages
Match supported package versions against known vulnerability data. Review severity, vulnerability identifiers and fixed versions when available.
Scan your ecosystem
Supported manifests and lockfiles include npm, Yarn, pnpm, pip, Poetry, Maven, Gradle, Go modules, NuGet, Composer, Bundler and Cargo. Include lockfiles where available for more precise version information.
Keep checking
Schedule recurring repository scans. New vulnerability disclosures can affect dependencies even when your own code has not changed.
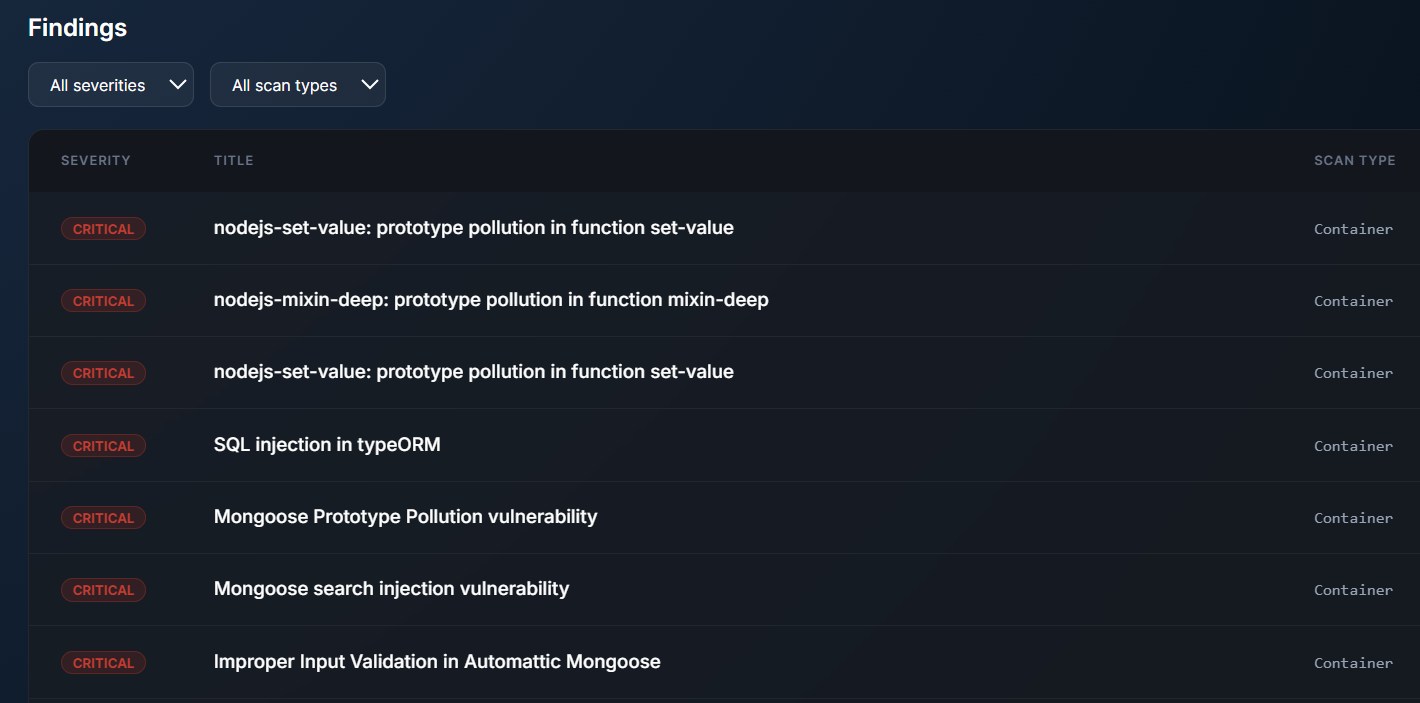
Package to finding
Know what needs attention.
Review affected packages in CYBERVOC and export their details and available remediation guidance as a PDF. Use the report to plan dependency updates with your team or external AI coding agent.
Explore scan coverage →