CVE Volume Is Exploding, But Remediation Speed Is the Real Vulnerability Crisis
What happened
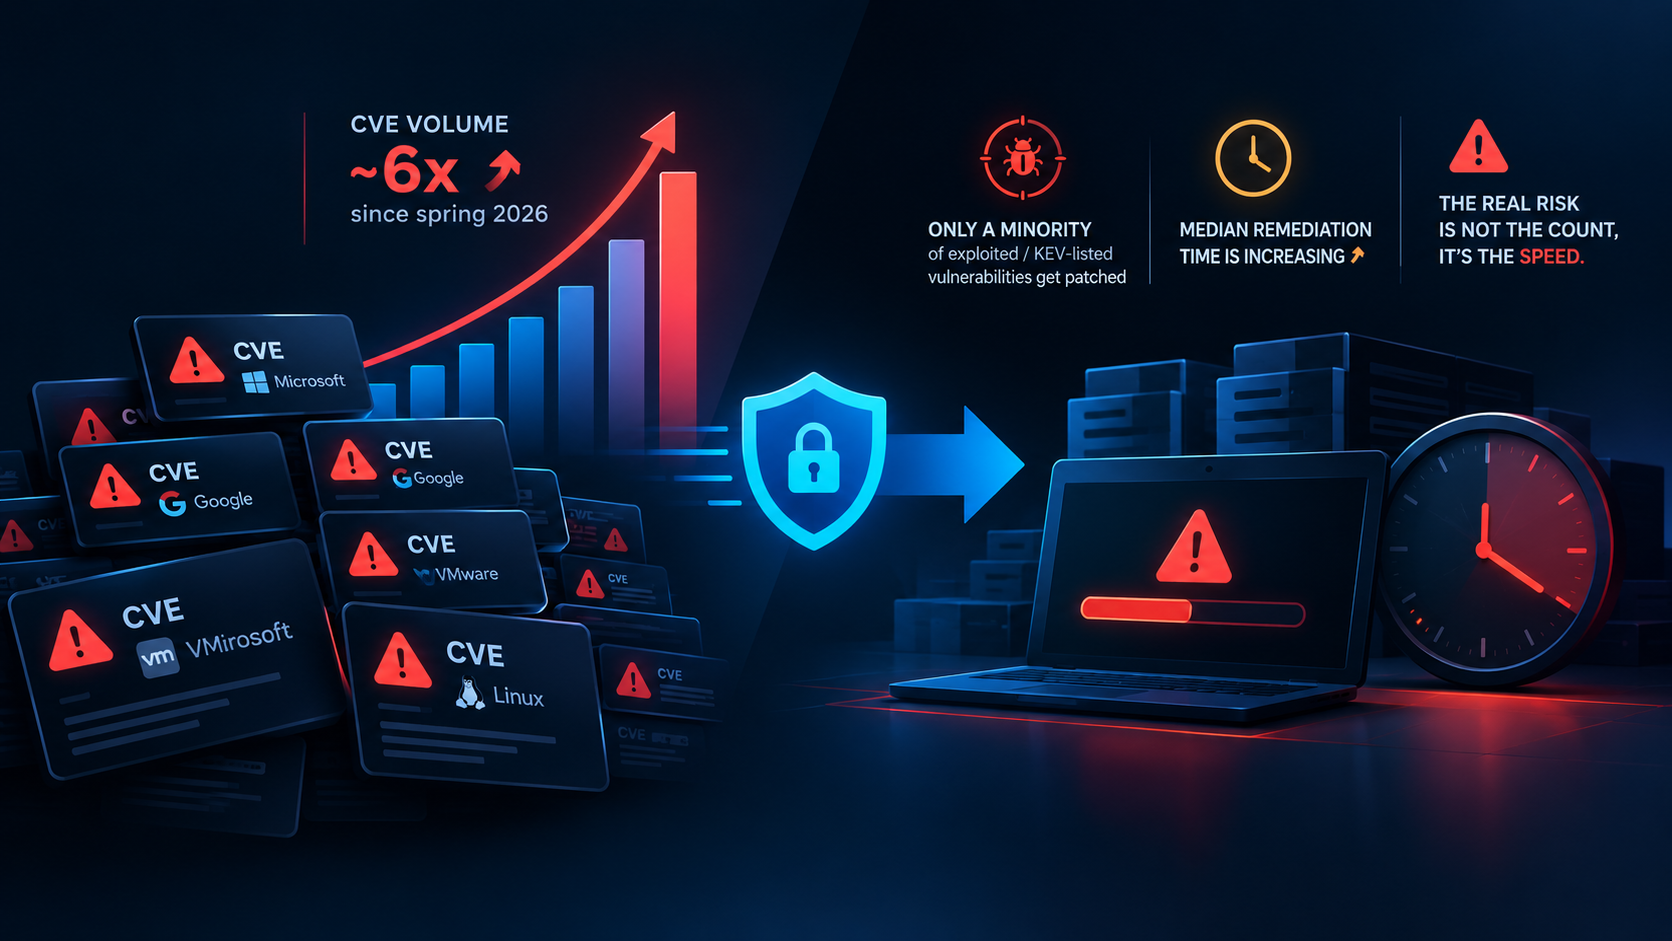
A widely circulated chart from venture firm a16z, built on data from Epoch AI, showed that critical and high-severity CVE disclosures across 21 major software vendors — including Apple, AWS, Microsoft, Google, and Adobe — stayed under roughly 100 per month for four years, then jumped to over 600 per month starting in spring 2026. The chart triggered two competing reactions online: one camp read it as evidence of a genuine spike in software risk, while the other pointed out that the number of vulnerabilities on CISA's Known Exploited Vulnerabilities (KEV) catalog has stayed relatively flat since 2024, implying that more disclosures do not automatically mean more real-world danger. Analysis from application security vendor Aikido argues both readings miss the more important signal: neither raw disclosure counts nor a flat KEV number determine actual risk on their own. What matters is how quickly organizations can determine which vulnerabilities are truly reachable and exploitable in their environment, and how fast confirmed issues actually get fixed. The prevailing explanation for the disclosure spike is that AI-assisted code review and vulnerability research tools are now finding real, long-standing bugs — including ones that survived years of manual review — faster than human reviewers can validate them, on both the defender and attacker side.
Who is affected
This trend affects essentially every organization that consumes software from large vendors, open-source ecosystems, or container base images, since the underlying driver is AI-accelerated vulnerability discovery across the industry rather than an issue specific to any one vendor or product. It has particular relevance for application security teams, vulnerability management programs, and anyone responsible for triaging and prioritizing CVE backlogs, including organizations that rely heavily on NVD scoring or vendor advisories as their primary source of vulnerability intelligence.
Why it matters
The disclosure spike has exposed a structural weakness in how the vulnerability ecosystem scores and prioritizes findings. NIST's National Vulnerability Database, long treated as an authoritative source for CVE scoring, has struggled to keep pace: a federal audit reportedly found its scoring backlog grew from around 13,000 to over 27,000 entries in eighteen months, prompting NIST to stop attempting to score every CVE and instead focus only on those tied to federal use, critical software, or entries already on the KEV list — with everything else effectively left unscored indefinitely. Even for vulnerabilities that clear every bar — confirmed, scored, and known to be under active exploitation — remediation is where organizations are falling behind. Industry research cited in the analysis found that only about a quarter of confirmed actively-exploited KEV vulnerabilities were fully remediated in 2025, a decline from the prior year, while the median time to fully patch a vulnerability increased by more than 10 days year over year. Even well-resourced organizations reportedly remediate only 30-40% of such vulnerabilities within the first week of disclosure. This creates what the analysis calls a "remediation paradox": the rate of new vulnerability discovery is accelerating while the rate of fixing is not keeping up, widening the exposure window for known, exploitable weaknesses. The analysis also highlights that vulnerabilities do not need an assigned CVE number or a formal vendor advisory to be real or actively exploited — waiting for either before acting can hand attackers a head start, since researchers have observed unauthenticated remote-code-execution issues being exploited in the wild before any CVE or advisory existed.
Technical details
- Disclosure trend: Critical/high CVEs across 21 major vendors rose from under 100/month to over 600/month starting spring 2026, per a16z and Epoch AI data.
- KEV catalog size: Reported as relatively flat since 2024, suggesting the spike is concentrated in disclosure volume rather than confirmed active exploitation.
- NIST/NVD backlog: Grew from roughly 13,000 to over 27,000 unscored entries in eighteen months per a cited federal audit; NIST has shifted to scoring only federal-use, critical-software, or KEV-listed CVEs.
- Remediation rates: Roughly one in four confirmed actively-exploited KEV vulnerabilities were fully remediated in 2025 (down from the prior year); median full-patch time increased to over 40 days.
- Root cause of the spike: Widely attributed to AI-assisted vulnerability discovery tools surfacing existing, previously unnoticed bugs faster than human review processes can validate and score them — not a sudden drop in software quality.
- No-CVE exploitation risk: At least one unauthenticated RCE affecting a widely used e-commerce platform was reportedly exploited before any CVE identifier or vendor advisory existed, illustrating that CVE assignment lags real-world risk.
Recommended actions
- Do not use raw CVE disclosure counts as a proxy for organizational risk; instead, track how quickly your team validates, prioritizes, and remediates vulnerabilities that are confirmed to be reachable and exploitable in your specific environment.
- Prioritize remediation using reachability and exploitability context (is the vulnerable code path actually invoked, is the package actually used in a way that exposes the flaw) rather than CVSS score or disclosure volume alone.
- Treat presence on CISA's KEV catalog as a hard prioritization signal, and measure your own KEV remediation rate and median time-to-patch as a core security metric — aim to beat the roughly 25-40% first-week remediation baseline reported industry-wide.
- Do not wait for a formal CVE number or vendor advisory before acting on credible reports of exploitation against software you run; build a process for triaging unconfirmed or pre-disclosure reports.
- Invest in automation for patching known-vulnerable open-source dependencies and container base images at the pinned version already in use, to reduce the operational cost of fast remediation.
- Maintain an accurate software inventory and SBOM coverage so that when a new disclosure or exploitation report emerges, you can immediately determine whether it applies to your environment without manual investigation.
- Revisit vulnerability management SLAs in light of rising median patch times industry-wide; if your remediation timelines are trending in the same direction, treat it as a process and tooling gap rather than an unavoidable trend.
Sources
- https://www.aikido.dev/blog/cve-spike-remediation-problem