CYBERVOC / Blog
Insights for a Safer Digital World.
Security research, practical guidance and a closer look at the code and dependencies we build with.
Developer Security
GitLab Urges Immediate Patch for Critical AI Gateway RCE (CVE-2026-90970)
GitLab disclosed a critical flaw in its AI Gateway that can allow command execution in self-hosted deployments under specific conditions. Security teams running self-managed gateways should prioritize upgrades, validate exposure, and monitor authentication and gateway logs for suspicious activity.
Patch Management
Critical FortiMail Flaw CVE-2026-104286 Under Active Exploitation
Fortinet disclosed a critical FortiMail vulnerability (CVE-2026-104286) reported as actively exploited. Organizations should rapidly patch exposed mail gateways, reduce internet exposure where possible, and review logs for suspicious file-write or post-compromise activity.
Cloud Security
Dell CSM Critical CVEs Expose Kubernetes Storage Control Planes
Dell patched multiple severe vulnerabilities in Container Storage Modules (CSM), including max-severity issues affecting authorization paths and privilege boundaries. Kubernetes operators using Dell-backed storage should patch quickly and validate cluster-level blast radius and access controls.
Threat Intelligence
Warlock Ransomware Campaign Expands SharePoint Exploitation in Critical Infrastructure
Researchers report continued Warlock activity abusing SharePoint vulnerabilities against critical infrastructure and public-sector targets. Defenders should prioritize SharePoint hardening, patch hygiene, identity controls, and rapid detection of post-exploitation behavior.
Vulnerabilities
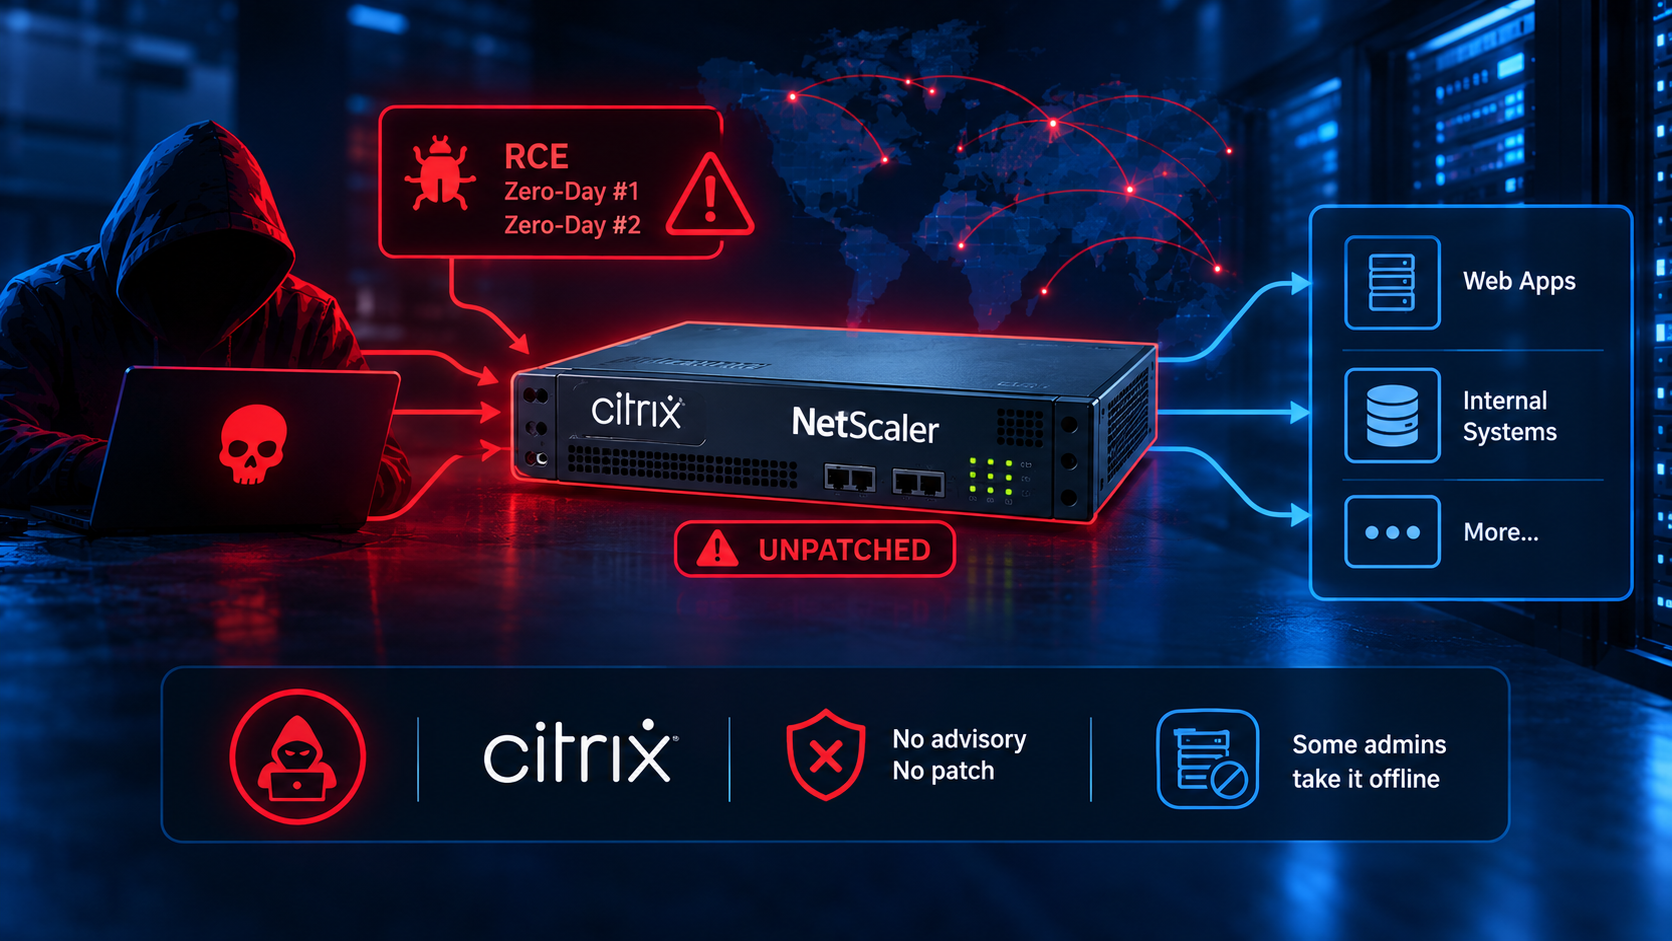
Two Unpatched Citrix NetScaler Zero-Days Under Active Exploitation
Security firm watchTowr says two new remote-code-execution zero-days in Citrix NetScaler ADC and Gateway are being exploited in the wild, with no vendor advisory or patch yet available. Some administrators are taking edge appliances offline; a fix is reportedly expected early next week.
Supply Chain Security
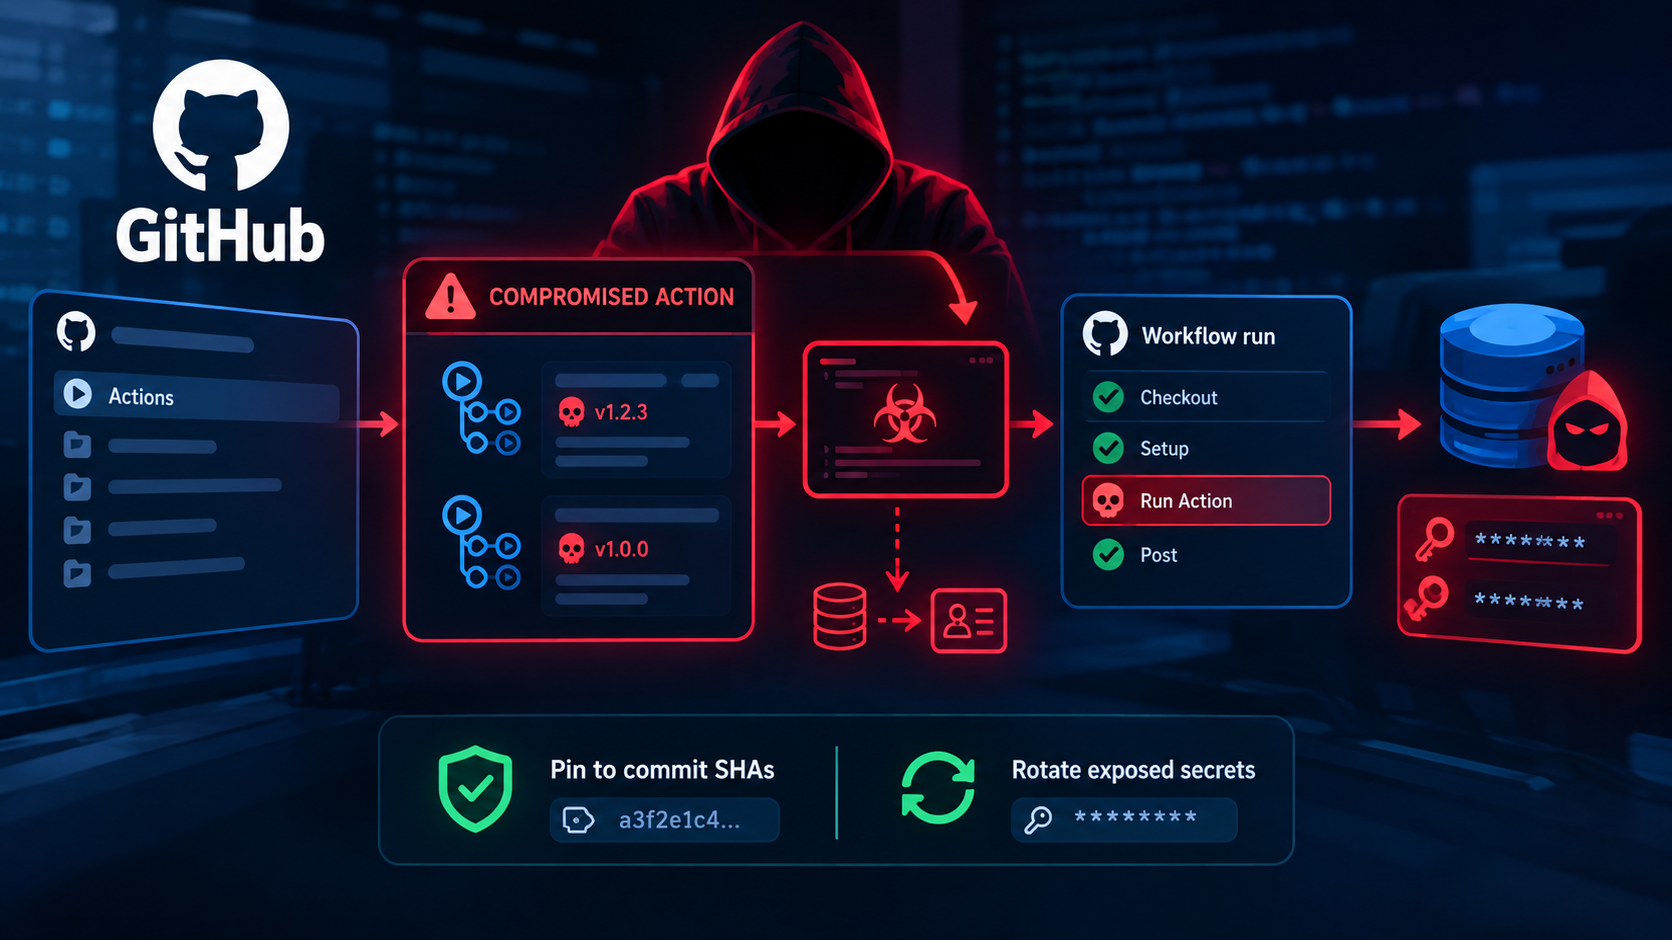
Compromised GitHub Actions Resurface, Silently Resume Serving Malware
Two GitHub Actions compromised in the May 2026 Mini Shai-Hulud campaign were re-enabled for over a week without their malicious release tags being cleaned up, causing referencing workflows to silently re-download and execute the original credential-stealing payload. Pin dependencies to commit SHAs and rotate any exposed CI/CD secrets.
Threat Intelligence
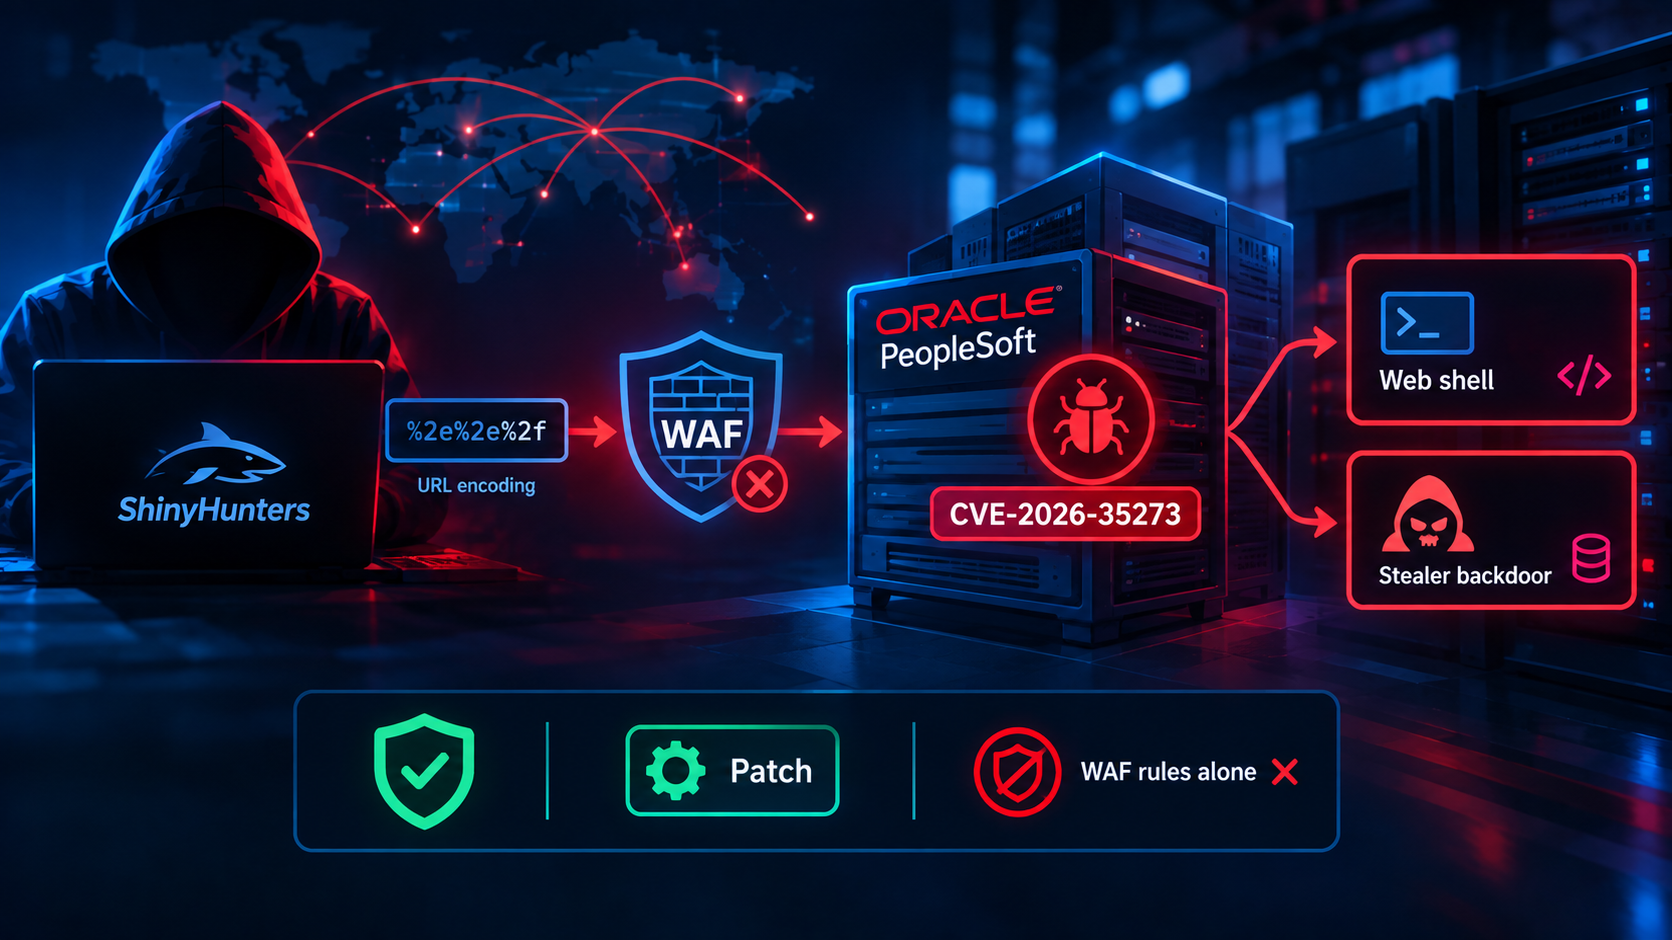
ShinyHunters Bypasses WAFs to Resume Mass Exploitation of Oracle PeopleSoft
Google reports the ShinyHunters-linked group UNC6240 is using a URL-encoding trick to bypass WAF rules protecting Oracle PeopleSoft's CVE-2026-35273 flaw, deploying web shells and a stealer backdoor across dozens of organizations worldwide. Patching, not WAF rules alone, is required to close the exposure.
Patch Management
CISA Flags SharePoint and MikroTik RouterOS Flaws as Actively Exploited
CISA has added a SharePoint code-injection flaw (CVE-2026-65660) and a MikroTik RouterOS authentication flaw (CVE-2026-67279) to its Known Exploited Vulnerabilities catalog after confirming real-world attacks. The RouterOS flaw is chained into the "MikroTrick" exploit for full unauthenticated router takeover — patch both immediately.
Patch Management
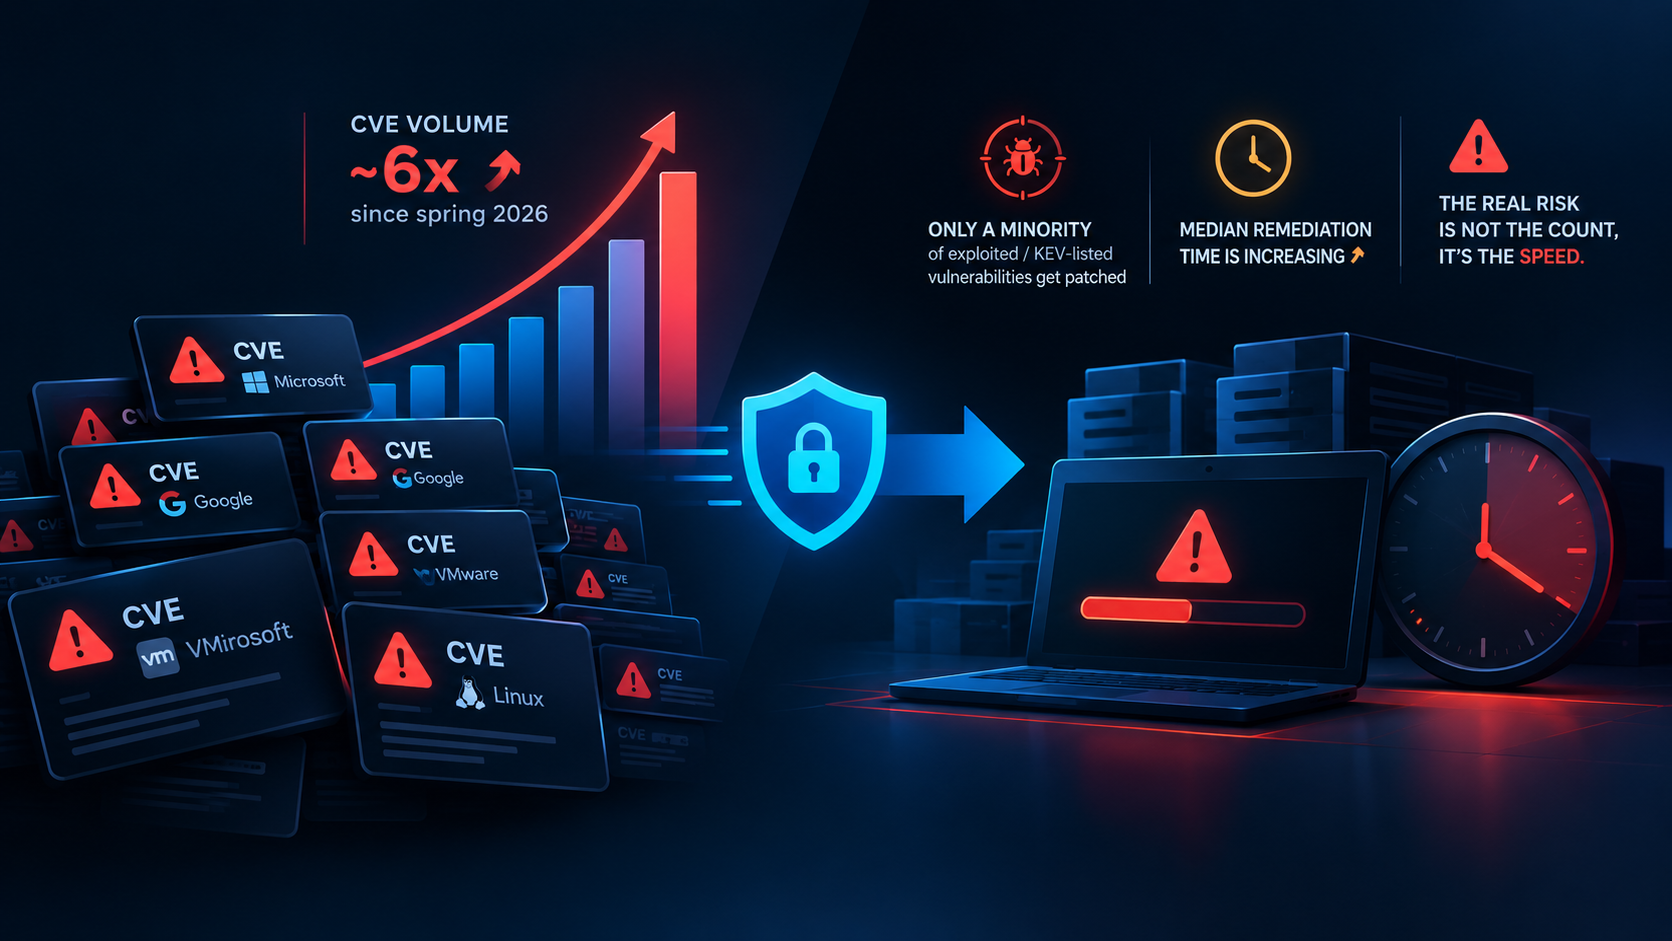
CVE Volume Is Exploding, But Remediation Speed Is the Real Vulnerability Crisis
Critical and high-severity CVE disclosures across major vendors have jumped roughly sixfold since spring 2026, but rising counts are not the real risk indicator. Industry data shows only a minority of actively exploited, KEV-listed vulnerabilities get fully patched, and median remediation time is increasing — teams should prioritize fix speed over raw CVE volume.
Vulnerabilities
Check Point Patches Two Critical VPN Certificate Flaws Amid Exploitation Warning
Check Point has patched two 9.8-rated VPN certificate vulnerabilities (CVE-2026-85102, CVE-2026-85103) that could allow unauthenticated remote code execution on Security Gateways and Management Servers. The Dutch NCSC warns exploitation is imminent even though no public proof-of-concept exists yet — apply Live Patch or Jumbo Hotfixes now.
Supply Chain Security
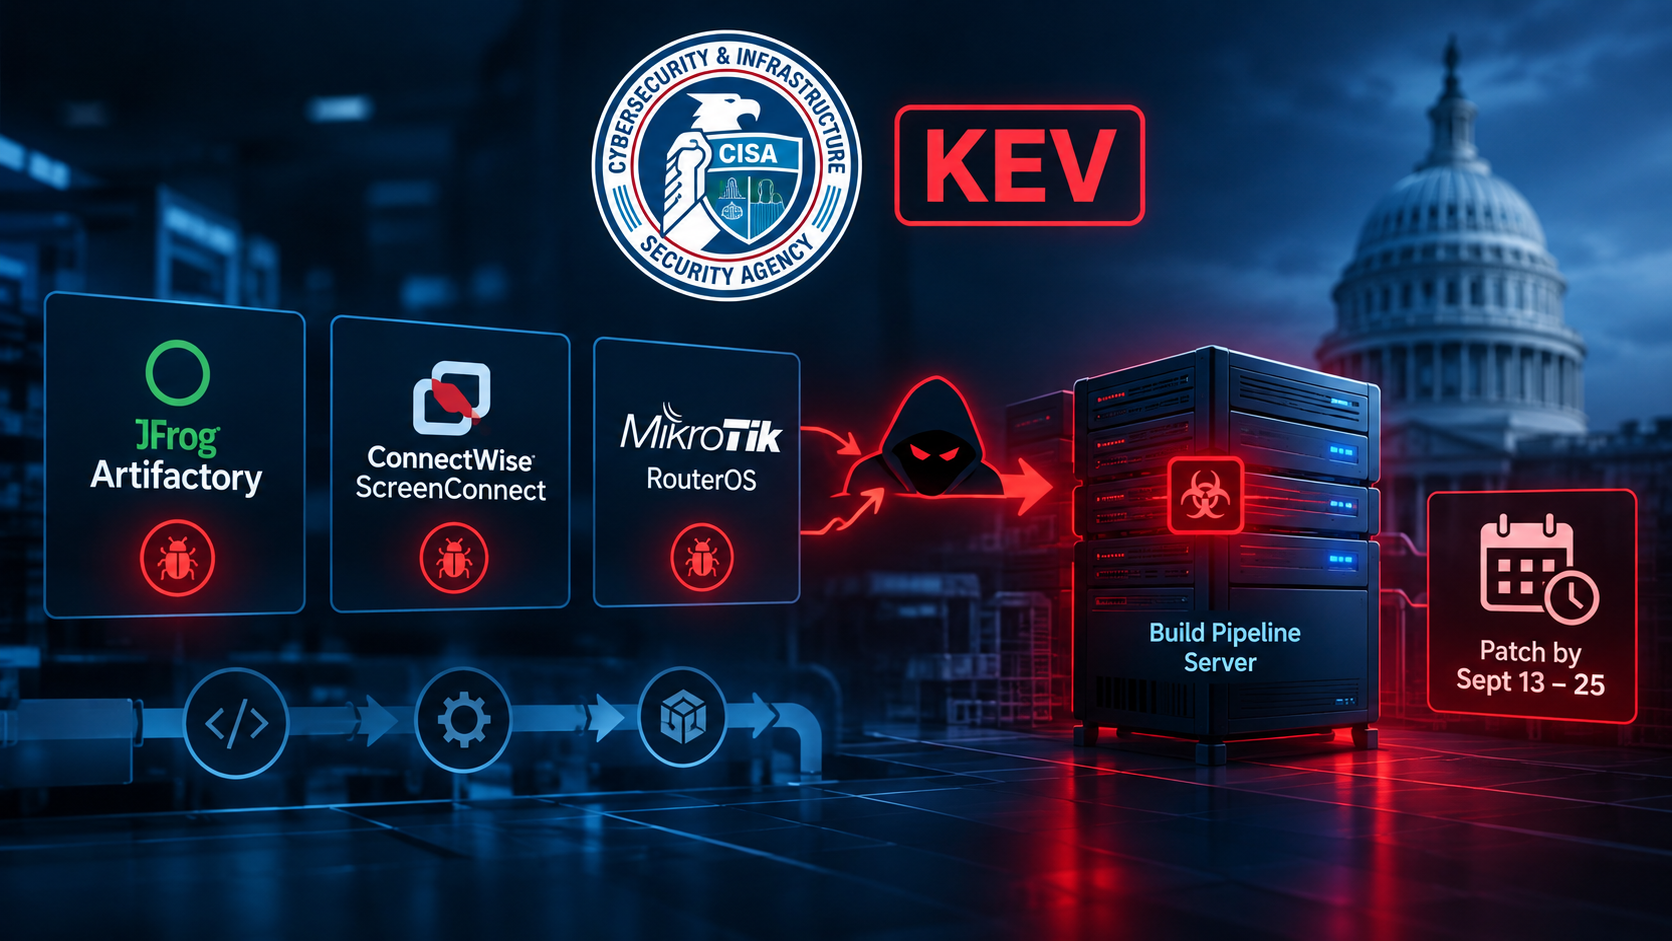
CISA Adds Five Actively Exploited Artifactory, ScreenConnect, RouterOS Flaws to KEV
CISA has added five actively exploited vulnerabilities affecting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS to its KEV catalog. Attackers are chaining Artifactory flaws to seize admin control and plant backdoors on unpatched build-pipeline servers. Federal patch deadlines fall between September 13 and 25.
Ransomware
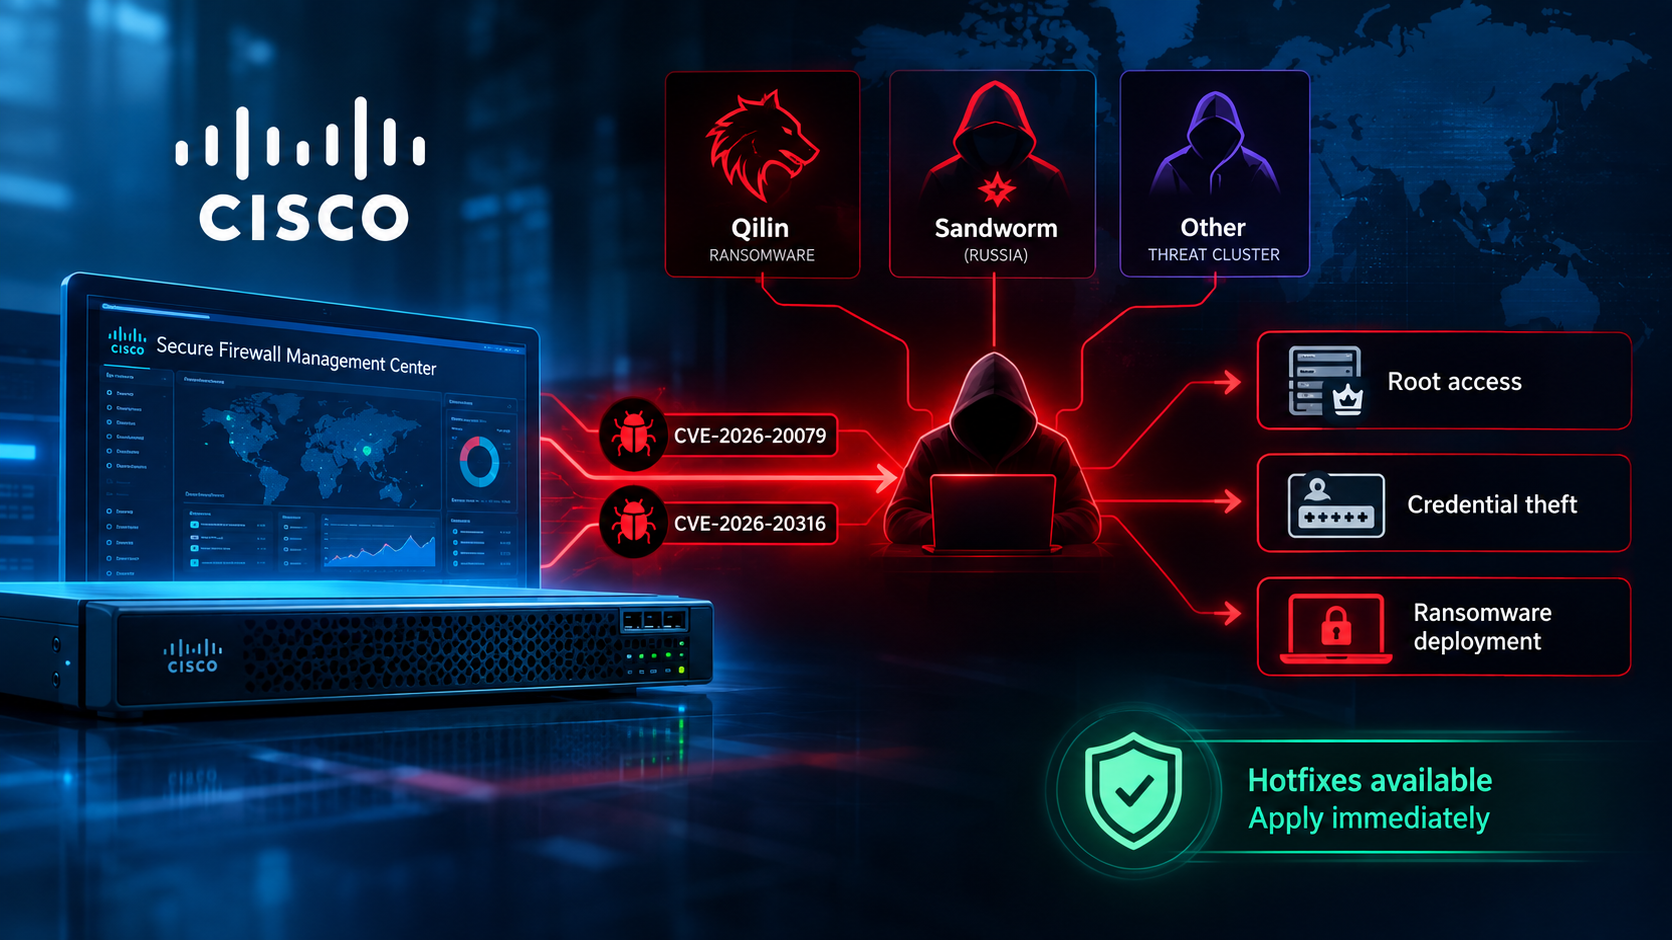
Cisco Secure FMC Flaws Exploited by Ransomware and State-Sponsored Hackers
Cisco Talos confirms three separate threat clusters — including Qilin ransomware affiliates and a group whose tooling overlaps with the Russian Sandworm actor — are exploiting two Secure Firewall Management Center flaws (CVE-2026-20079, CVE-2026-20316) for root access, credential theft, and ransomware deployment. Hotfixes are available; apply immediately.
Developer Security
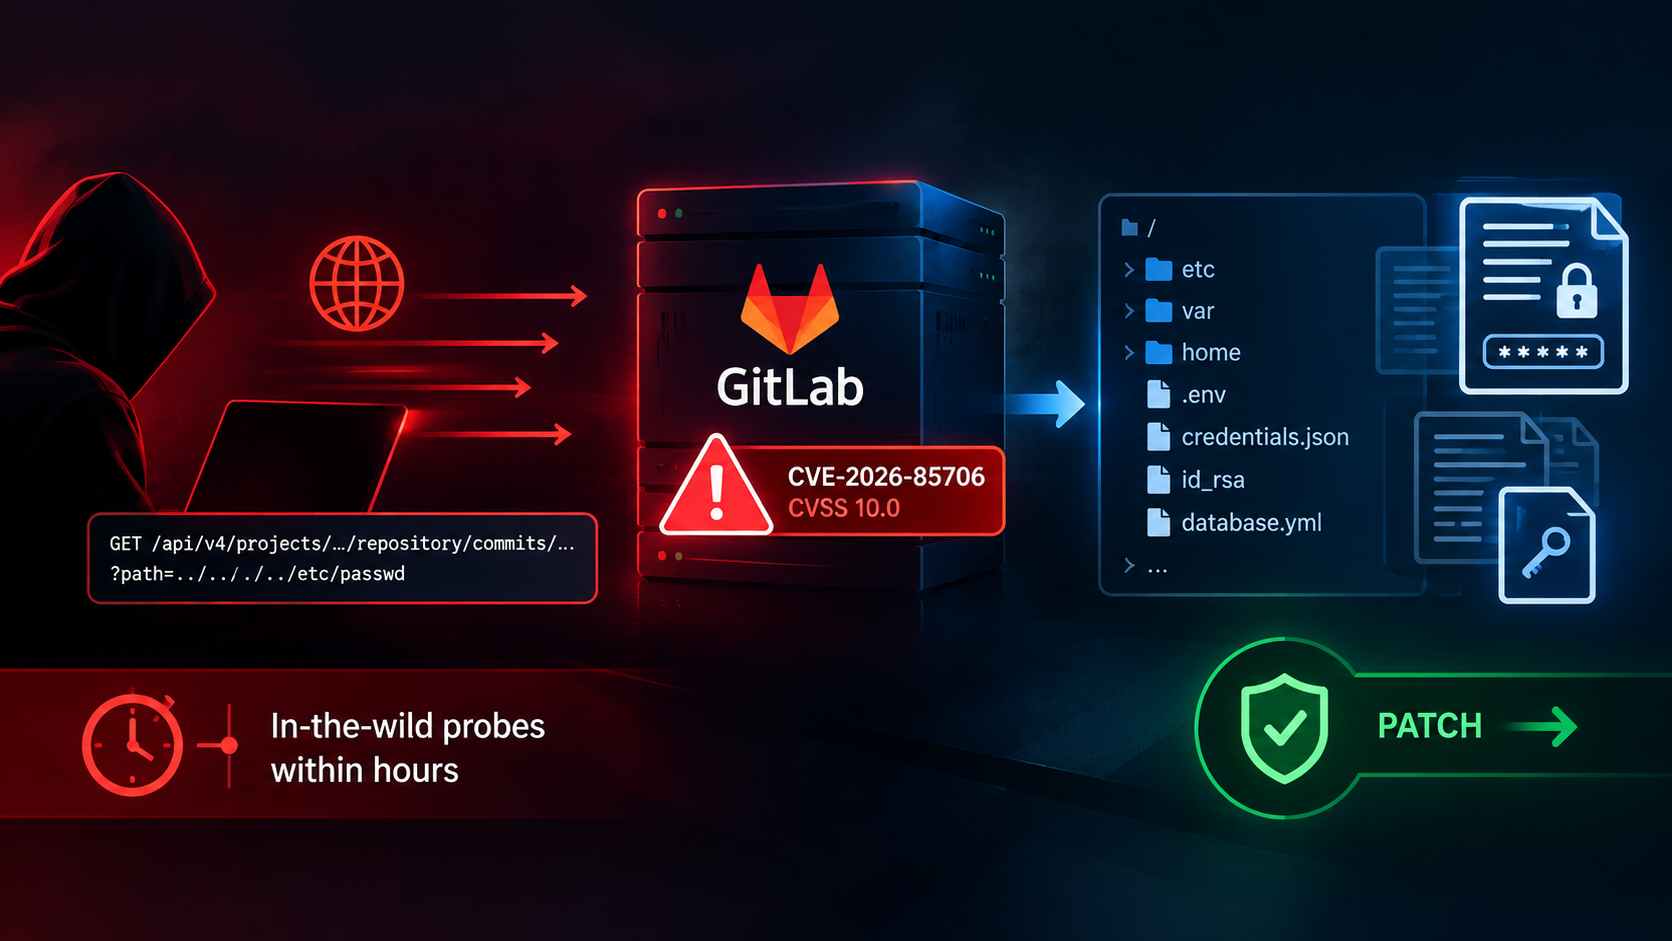
GitLab CVSS 10 Path Traversal Flaw Draws In-the-Wild Probes Within Hours
GitLab has patched a maximum-severity path traversal flaw (CVE-2026-85706, CVSS 10.0) in its repository commits API that lets unauthenticated attackers read arbitrary files, including credentials and secrets. In-the-wild scanning began within hours of disclosure — self-managed instances should be patched immediately.
Vulnerability Management
CVE-2026-82329: JFrog Artifactory Already Exploited, Priority Patching for DevSecOps Teams
The critical CVE-2026-82329 flaw (CVSS 9.8) in JFrog Artifactory is already being exploited just days after disclosure. This briefing covers impacted versions, supply-chain risk, and an actionable containment plan.
AI Security
Langflow CVE-2026-0768: Active Key-Theft Campaign Demands Immediate Cloud Secret Rotation
Attackers are exploiting CVE-2026-0768 in Langflow to extract OpenAI and AWS credentials. This update summarizes the current threat, likely blast radius, and urgent defensive actions for platform and SecOps teams.
Supply Chain Security
Virtualizor: BGP Hijack Targeted the Update Chain, Trust Controls Need Hardening
A BGP routing hijack enabled delivery of a malicious Virtualizor update during a limited exposure window. Here is a defensive analysis and a practical risk-reduction plan for hosting and operations teams.
Cloud Security
ServiceNow AI Platform: Three CVSS 10.0 Flaws Require Immediate Patching
ServiceNow disclosed three unauthenticated, low-complexity vulnerabilities in its AI Platform, each rated CVSS 10.0. Hosted instances were patched by the vendor, but self-hosted customers should urgently deploy the released hotfixes and validate exposure paths for code and SQL injection risks.
Vulnerabilities
PaperCut NG/MF Zero-Day Chain: Emergency Patch Release 2 Is Now Required
PaperCut confirmed active exploitation and issued a second emergency update after researchers found bypasses in the first fix. Organizations running PaperCut NG/MF should deploy Release 2 immediately, restrict web admin exposure, and review indicators tied to pre-auth compromise attempts.
Patch Management
Citrix NetScaler CVE-2026-8452: KEV Listing Signals Urgent Remediation
CVE-2026-8452 in Citrix NetScaler is now in CISA KEV after reports of in-the-wild exploitation. Teams using affected AAA or Gateway VPN configurations should patch immediately and investigate appliances for unauthorized changes and suspicious command execution patterns.
Developer Security
Next.js Security Update: Critical AVIF and Windows RCE Risks Patched
Vercel patched two critical Next.js vulnerabilities that can lead to unauthenticated remote code execution under specific conditions, including Windows-hosted deployments and AVIF optimization paths. Engineering teams should upgrade immediately to patched LTS versions and review image-processing exposure.
Vulnerabilities
GitLab CVE-2026-19478: Active Exploitation Targets Public Projects
A critical GitLab code-injection flaw (CVE-2026-19478) is already being exploited against internet-facing instances. Organizations should urgently patch affected versions, review GraphQL access controls, and hunt for suspicious requests tied to exploitation attempts.
Patch Management
CISA Orders Emergency Patching for Actively Exploited Zimbra RCE
CISA added CVE-2026-73570 to KEV and required rapid mitigation due to active exploitation of Zimbra Collaboration Suite. Security teams should prioritize upgrades to fixed versions, validate SNMP exposure, and investigate signs of compromise on mail servers.
Developer Security
Critical Keycloak CVE-2026-18963 Enables Account Takeover via Reset Flow
A critical Keycloak password-reset vulnerability (CVE-2026-18963) may allow unauthenticated account takeover in vulnerable deployments. Teams should upgrade to fixed releases immediately and disable 'Forgot password' temporarily if patching cannot be completed at once.