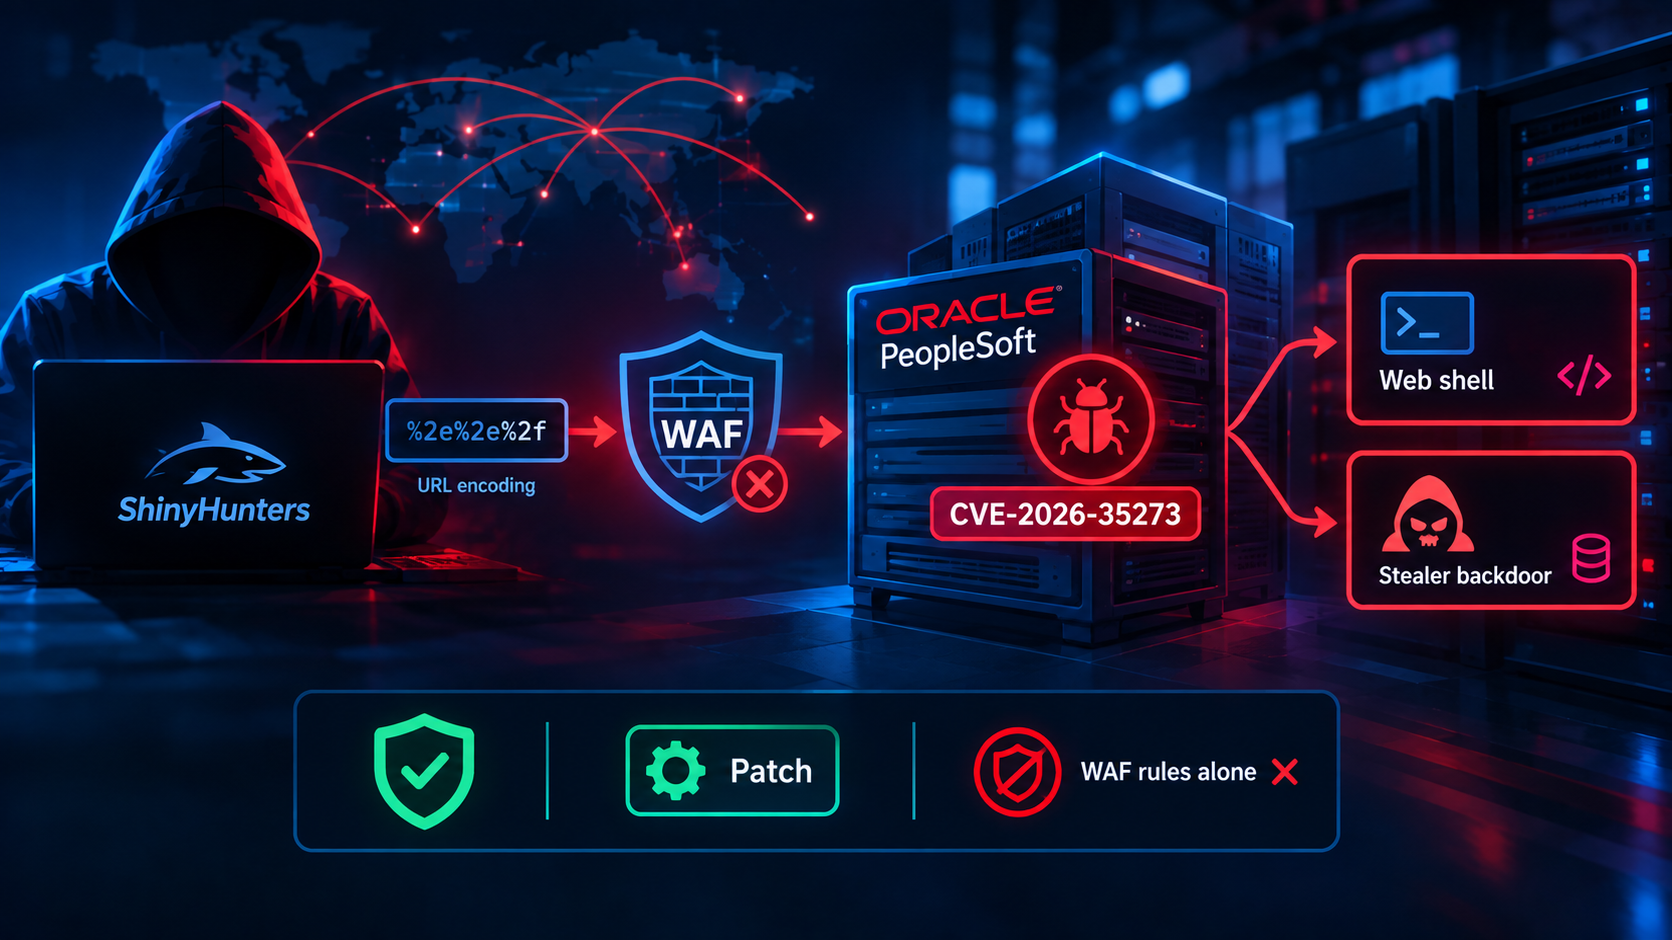
ShinyHunters Bypasses WAFs to Resume Mass Exploitation of Oracle PeopleSoft
What happened
Google's Mandiant and Threat Intelligence Group have detailed a renewed wave of mass exploitation against Oracle PeopleSoft servers, driven by the ShinyHunters-linked threat cluster UNC6240 modifying its exploit for CVE-2026-35273 to bypass web application firewall (WAF) protections. The vulnerability itself is not new — it was first exploited as a zero-day in mid-2026 against academic institutions and fixed by Oracle shortly after. Many organizations that could not immediately apply the patch instead relied on WAF rules to block requests to the vulnerable /PSEMHUB/ endpoint. Mandiant now reports that attackers are getting around those rules with a simple but effective trick: percent-encoding a single character in the request path (sending /%50SEMHUB/ instead of /PSEMHUB/, where %50 is the encoded form of the letter "P"). Many WAFs and reverse proxies inspect the literal, un-decoded request path, so a rule written to block /PSEMHUB/ simply does not match the encoded variant — while the PeopleSoft application server itself decodes the path before routing, sending the request straight to the vulnerable component anyway.
Who is affected
Organizations running Oracle PeopleSoft that have not applied the security update for CVE-2026-35273, and that relied solely on WAF-based blocking of the /PSEMHUB/ path as a substitute for patching, remain exposed to this bypass. Google reports that the current wave of attacks spans higher education, technology, IT services, healthcare, agriculture, transportation, and government sectors globally, with web shells deployed on dozens of systems. Google also warns that ShinyHunters may not stick to the single %50 variant observed so far, and could rotate through other percent-encoded, mixed-case, or otherwise obfuscated forms of the path to continue evading detection.
Why it matters
This case is a clear demonstration of why compensating controls like WAF rules are not a substitute for patching a known, actively exploited vulnerability — they can reduce but do not eliminate risk, and attackers actively probe for and defeat them. It is also notable for how methodical the reconnaissance-before-exploitation process is: Mandiant describes the attackers sending a handful of preliminary requests carrying serialized Java objects that return host information without writing files or disrupting service, letting them silently confirm exploitability before committing to a full attack. ShinyHunters (tracked by Google as UNC6240) has an established pattern of data theft for extortion, so affected organizations should anticipate follow-on extortion contact and the possibility that stolen data will be published or sold if a ransom demand is not met. This story runs alongside separate, so-far-unverified ShinyHunters claims of a different, undisclosed PeopleSoft zero-day used in a high-profile breach; that claim is unconfirmed and distinct from the well-documented CVE-2026-35273 exploitation described here.
Technical details
- CVE-2026-35273 — CVSS 9.8. Unauthenticated remote code execution in Oracle PeopleSoft's Environment Management Hub (PSEMHUB) component; patched by Oracle after being exploited as a zero-day.
- Bypass technique: Percent-encoding a character in the request path (e.g.,
/%50SEMHUB/hubinstead of/PSEMHUB/hub) to evade WAF rules that match on the literal, undecoded path, while the PeopleSoft/WebLogic stack decodes and routes the request normally. - Attack chain: Reconnaissance via POST requests with serialized Java objects to fingerprint vulnerable hosts, followed by abuse of Java deserialization in the PSEMHUB servlet to deploy JSP web shells (
x.jspfor command execution,u.jsp/u2.jspfor chunked file uploads). - Follow-on payloads: A trojanized, signed installer (
Ple64.exe) that loads an in-memory backdoor Google tracks as SIDEEYE, capable of browser/desktop credential theft, file and process management, and reverse proxy/reverse shell functionality; the open-source Neo-reGeorg tunneling toolkit for lateral movement; and the legitimate MeshAgent remote management tool for persistence on Linux hosts. - Privilege level: Google reports roughly a quarter of observed attacker commands executed as root or NT AUTHORITY\SYSTEM, with the remainder run under PeopleSoft or WebLogic service accounts.
- Threat actor: UNC6240, associated with the ShinyHunters extortion brand.
Recommended actions
- Apply Oracle's security update for CVE-2026-35273 as the primary remediation; do not rely on WAF rules alone, as this campaign demonstrates they can be bypassed.
- Where the update cannot be applied immediately, disable the Environment Management Hub (EMHub) service in multi-server configurations, or remove the PSEMHUB application entirely in single-server deployments.
- Search WebLogic access logs for requests to
/PSEMHUB/and percent-encoded, mixed-case, or otherwise obfuscated variants of that path, not just the literal string. - Inspect the
PSEMHUB.wardirectory for unexpected JSP files (particularlyx.jsp,u.jsp,u2.jsp,tunnel.jsp,tunnel.jspx) and other unrecognized artifacts. - Rotate credentials accessible to the PeopleSoft application service account, and review database audit logs for bulk queries or exports against HR, payroll, or student-record tables.
- Monitor outbound traffic from PeopleSoft hosts for signs of tunneling or reverse-proxy activity, and prepare an extortion-response plan given ShinyHunters' established data-theft-for-ransom pattern.
Sources
- https://thehackernews.com/2026/09/attackers-bypass-wafs-to-exploit-oracle.html
- https://www.bleepingcomputer.com/news/security/shinyhunters-uses-waf-bypass-trick-in-oracle-peoplesoft-attacks/